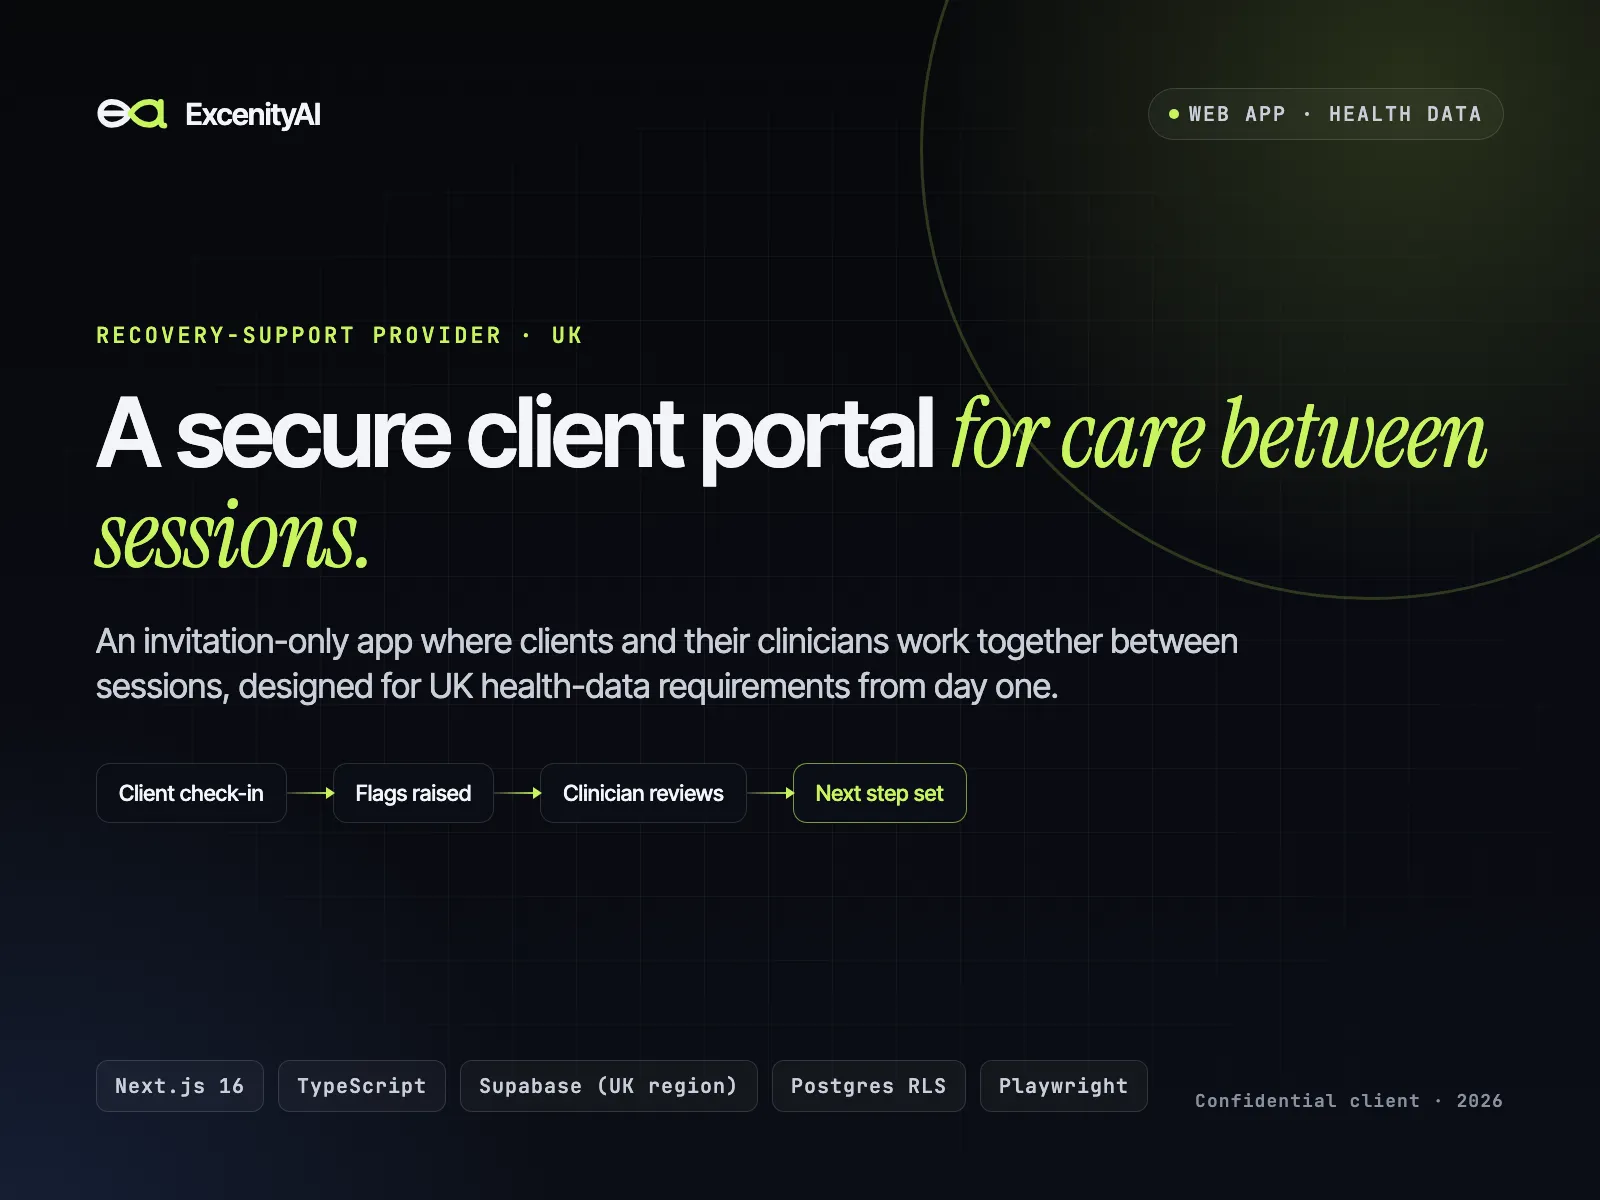
Secure client-clinician portal for a UK recovery service
We built an invitation-only mobile web app where a UK recovery-support provider's clients work with their clinicians between sessions. It is designed for UK health-data requirements, with Row Level Security on every table backed by 439 database tests. It is built for a pilot starting in January 2027.
By ExcenityAI · Published
The challenge
Between sessions, work between clients and clinicians was scattered across tools. Staff chased check-ins by hand. Health data needed to stay inside a secure, UK-hosted system.
How it works
- 01ClientsCheck-ins, goals and habits, assigned work, messages, sessions and progress in a mobile app.
- 02Urgent support everywhereA visible urgent-support path on every screen, even offline.
- 03CliniciansAn attention list of flagged clients, caseload, timelines and review of submitted work.
- 04Escalation with notesFlags can be reviewed or escalated, with a required note for the record.
- 05AdminsInvitations, allocations, group sessions, a resource library, attendance and records.
- 06Reports and exportOperational and anonymized evaluation reports with safe CSV export.
What we delivered
439 database security tests
Row Level Security on every table, keyed on role, allocation and MFA, tested with pgTAP.
Staff MFA and audit log
Authenticator-app MFA with recovery codes and an append-only audit trail.
Health content kept out of channels
Nothing sensitive in emails, push notifications, logs or URLs, with UK data residency.
Accessible
A WCAG 2.2 AA target, automated accessibility checks and contrast-tested colors.
Fast test suite
The end-to-end suite was restructured from 55.5 to about 2.5 minutes with no loss of coverage.
Security review
A pre-launch security review of every database migration and privileged function.
Stack
- Next.js 16
- TypeScript
- Supabase (UK region)
- Postgres RLS
- Playwright
- Vercel
- AWS SES
- Web Push
Related service: Apps & platforms